Table of Contents
In today’s hyper-connected business landscape, the thought of sensitive financial records, proprietary client data, or strategic intellectual property falling into the wrong hands isn’t just a nightmare—it’s an all-too-possible reality. A single, unencrypted external drive lost in transit or stolen from an employee’s bag can trigger catastrophic breaches, eroding hard-earned trust, inviting crippling regulatory fines, and potentially sinking a business overnight. The question isn’t if you need robust data protection for portable storage, but how to implement it effectively without sacrificing the operational agility your team demands. As cyber threats evolve with alarming sophistication, relying on basic password protection or software-only encryption is like locking your front door but leaving the vault wide open.
This guide cuts through the noise to focus squarely on what truly matters for businesses selecting encrypted external storage in 2026: actionable intelligence on features, security architectures, and deployment strategies that deliver genuine peace of mind. Forget fleeting product trends; we’re diving deep into the foundational elements that separate adequate security from true enterprise-grade resilience. Whether you’re safeguarding healthcare records bound by stringent HIPAA rules, financial data under GDPR scrutiny, or next-generation R&D blueprints, understanding these core principles is non-negotiable for making a future-proof investment that aligns with your risk profile and operational workflow. Let’s unpack what real security looks like beyond the marketing buzzwords.
Top 10 Encrypted External Hard Drives for Business
Detailed Product Reviews
1. Apricorn 2TB Aegis Padlock USB 3.0 256-Bit AES XTS Hardware Encrypted Portable External Hard Drive (A25-3PL256-2000)

Overview:
The Apricorn 2TB Aegis Padlock delivers military-grade security in a compact, bus-powered portable drive. Designed for users prioritizing data protection, it features 256-bit AES-XTS hardware encryption validated under FIPS PUB 197, eliminating software dependencies. Its PIN-based access simplifies secure usage without administrative rights.
What Makes It Stand Out:
True hardware encryption with FIPS validation ensures robust defense against breaches. The intuitive keypad PIN system, brute-force attack countermeasures (wiping data after 10 failed attempts), and epoxy-sealed tamper resistance set it apart. Administrator/user password separation adds enterprise-grade control.
Value for Money:
Priced higher than standard drives, it justifies cost for security-sensitive users (e.g., legal, healthcare). Competing software-encrypted solutions often lack FIPS validation or require complex setup, making this a cost-effective investment for uncompromised security.
Strengths and Weaknesses:
Strengths: Unbeatable physical security; truly plug-and-play; no driver installs; durable epoxy casing; reliable 5400 RPM performance.
Weaknesses: Limited to 2TB capacity; slower transfer speeds than non-encrypted SSDs; no macOS native support without reformatting.
Bottom Line:
Essential for professionals needing FIPS-validated, user-friendly encryption. While premium-priced, its zero-software design and tamper-proofing offer unmatched value for high-risk data environments. Highly recommended for security-first users.
2. Apricorn 500GB Aegis Padlock USB 3.0 256-bit AES XTS Hardware Encrypted Portable External Hard Drive (A25-3PL256-500)
Overview:
This compact 500GB Aegis Padlock prioritizes portability and ironclad security. Leveraging USB 3.0 speeds and FIPS 197-validated 256-bit AES-XTS encryption, it’s ideal for securing sensitive files on the go without software installs or admin rights.
What Makes It Stand Out:
Its military-grade epoxy coating repels physical attacks, while the self-destruct feature instantly erases data after 10 incorrect PIN attempts. The software-free design ensures cross-platform compatibility (Windows/macOS/Linux), and USB 3.0 delivers up to 10x faster transfers than USB 2.0.
Value for Money:
Though the 500GB capacity feels modest today, it’s competitively priced for ultra-secure, portable storage. Cheaper encrypted drives often lack FIPS validation or brute-force protection, making this a smart buy for critical small-data use cases like financial records or credentials.
Strengths and Weaknesses:
Strengths: Impenetrable physical security; true cross-platform usability; intuitive PIN access; tamper-evident epoxy seal; rapid USB 3.0 transfers.
Weaknesses: Low storage capacity; not cost-effective for bulk data; slower than SSD alternatives; bus-power limits use with some older ports.
Bottom Line:
A niche powerhouse for securing small, high-value datasets. If you need maximum portability with enterprise-grade encryption for critical files, this excels despite its capacity limitations. Best for targeted security needs.
3. Apricorn 4TB Aegis Fortress L3- FIPS Level 3 Validated USB 3.0 Hardware Encrypted Portable Drive (AFL3-4TB)

Overview:
The Aegis Fortress L3 4TB represents Apricorn’s pinnacle of rugged, high-capacity encryption. FIPS 140-2 Level 3 validated, it combines 256-bit AES-XTS security with exceptional durability for users handling classified or highly sensitive data in demanding environments.
What Makes It Stand Out:
FIPS Level 3 certification signifies resistance to physical penetration (e.g., probes, disassembly), surpassing standard FIPS 197 drives. Dual read-only modes prevent data alteration, while separate admin/user PINs enable granular access control. Its reinforced casing withstands drops and extreme conditions.
Value for Money:
Premium-priced but justified for regulated industries (government, defense). Competing FIPS Level 3 drives are scarce and often less user-friendly. The 4TB capacity offers better cost-per-terabyte than smaller encrypted models, ideal for large secure datasets.
Strengths and Weaknesses:
Strengths: Unrivaled FIPS Level 3 physical security; versatile read-only modes; admin/user separation; exceptional ruggedness; fast USB 3.0 throughput.
Weaknesses: Heavier than standard portable drives; requires robust USB-C adapter for newer laptops; limited macOS optimization; higher cost than non-validated alternatives.
Bottom Line:
The gold standard for mission-critical portable encryption. If FIPS Level 3 compliance and brute-force defense are non-negotiable, this 4TB powerhouse is worth every penny for enterprise or government use.
4. Apricorn 5TB Aegis Fortress L3- FIPS Level 3 Validated USB 3.0 Hardware Encrypted Portable Drive (AFL3-5TB)
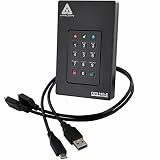
Overview:
Apricorn’s 5TB Aegis Fortress L3 elevates secure storage with massive capacity and FIPS 140-2 Level 3 validation. Built for professionals managing voluminous sensitive data, it merges military-grade encryption with ruggedized durability for uncompromised field security.
What Makes It Stand Out:
Like its 4TB sibling, it boasts FIPS Level 3 certification for tamper resistance, dual read-only modes, and admin/user PIN separation. The expanded 5TB capacity handles extensive datasets (e.g., engineering files, surveillance footage) while maintaining brute-force attack protection and epoxy-sealed integrity.
Value for Money:
Offers superior cost-per-terabyte for encrypted storage. While pricier than consumer drives, its FIPS Level 3 certification—which mandates rigorous physical security testing—is rare at this capacity. Cheaper alternatives risk compliance gaps in regulated sectors.
Strengths and Weaknesses:
Strengths: Industry-leading FIPS Level 3 security; generous 5TB capacity; dual read-only modes; resilient construction; seamless Windows integration.
Weaknesses: Bulky design; macOS requires reformatting; premium cost; USB 3.0 cable not USB-C native (adapter needed).
Bottom Line:
The definitive choice for high-capacity, ultra-secure portable storage. If your work demands FIPS Level 3 compliance and 5TB of encrypted space, this drive delivers unmatched reliability for critical infrastructure or defense applications.
5. WD 20TB Elements Desktop External Hard Drive, USB 3.0 drive for plug-and-play storage - WDBWLG0200HBK-NESN

Overview:
The WD 20TB Elements Desktop is a high-capacity, budget-friendly solution for bulk storage needs. Designed for straightforward plug-and-play use with Windows, it offers massive space for backups, media libraries, or archival without complex setup.
What Makes It Stand Out:
Its standout feature is the enormous 20TB capacity at an accessible price point. USB 3.0 ensures fast transfers for large files, while WD’s reliability pedigree provides peace of mind. The simple desktop form factor suits home or office environments prioritizing volume over portability.
Value for Money:
Exceptional value for pure storage volume. At roughly half the cost-per-terabyte of encrypted alternatives, it’s ideal for non-sensitive data like photos, videos, or game libraries. However, it lacks encryption or advanced features, so security-conscious users should look elsewhere.
Strengths and Weaknesses:
Strengths: Unbeatable capacity-to-cost ratio; reliable WD build quality; effortless Windows setup; quiet operation; fast USB 3.0 transfers.
Weaknesses: Requires external power adapter; macOS needs reformatting; no hardware encryption; not portable; basic durability.
Bottom Line:
A no-frills workhorse for affordable, high-volume storage. Perfect for expanding home media servers or Windows backups where security isn’t critical. Avoid for sensitive data, but unmatched for raw capacity on a budget.
6. Kingston IronKey Vault Privacy 80 960GB External SSD | FIPS 197 | XTS-AES 256GB Encrypted | Touch Screen PIN | Secure Data Protection | IKVP80ES/960G

Overview:
This high-capacity external SSD delivers military-grade security for sensitive data, featuring FIPS 197 certification and XTS-AES 256-bit encryption. Designed for professionals requiring robust protection against physical and digital threats.
What Makes It Stand Out:
The intuitive touch-screen interface for PIN entry eliminates keylogger risks, while dual-password modes (Admin/User) enable granular access control. Unique configurable password rules and dual write-protect modes provide exceptional malware resistance, distinguishing it from basic encrypted drives.
Value for Money:
Priced premium for its 960GB capacity and advanced security suite, it justifies cost for regulated industries (e.g., healthcare, government) where data breaches incur severe penalties. Competitors often lack touch-screen convenience or comparable tamper resistance at this capacity.
Strengths and Weaknesses:
Strengths: Unmatched 960GB secure storage; intuitive touch-PIN; admin/user separation; write-protect modes enhance security; durable build.
Weaknesses: Higher cost than non-touch alternatives; FIPS 197 (algorithm-only) vs. full FIPS 140-2 validation; limited to USB 3.2 Gen 2 speeds.
Bottom Line:
Essential for enterprises needing high-capacity, tamper-proof storage with user-friendly security. Despite the price, its specialized features make it a top-tier investment for critical data protection.
7. Integral 4GB Crypto-197 256-Bit 3.0 USB Flash Drive Encrypted - FIPS 197 Certified, Brute Force Password Attack Protection & Waterproof Double Layer Design

Overview:
A compact, ultra-secure USB 3.0 flash drive targeting budget-conscious users needing basic military-grade encryption in a portable form factor, certified to FIPS 197 standards.
What Makes It Stand Out:
Its auto-erase function after six failed password attempts thwarts brute-force attacks decisively. The dual-layer waterproof design (silicone outer + hardened inner case) offers rare physical durability for encrypted drives, ideal for fieldwork or harsh environments.
Value for Money:
Exceptional value under $30 for FIPS 197 certification and brute-force protection. While capacity is limited (4GB), it outperforms similarly priced competitors with its waterproofing and auto-lock features, suiting document-only workflows.
Strengths and Weaknesses:
Strengths: Affordable security; robust waterproof/drop-proof build; auto-erase security; simple alphanumeric password; OS-agnostic.
Weaknesses: Very low 4GB capacity; FIPS 197 only (not full module validation); no admin/user roles; slower speeds than SSDs.
Bottom Line:
A niche but compelling choice for low-capacity, high-risk scenarios like emergency data transport. Best for users prioritizing physical resilience over storage space.
8. Apricorn ASK3-NX 32GB USB 3.1 Encrypted Secure Drive (ASK3-NX-32GB)

Overview:
A no-software, hardware-encrypted USB drive validated to FIPS 140-2 Level 3—the highest U.S. government standard for physical and logical security—ideal for air-gapped or restricted systems.
What Makes It Stand Out:
FIPS 140-2 Level 3 certification ensures rigorous tamper resistance and zero data leakage to host systems. Its OS-agnostic operation (Windows/Mac/Linux) and embedded PIN pad prevent keylogging, while dual read-only modes block malware injection during transfers.
Value for Money:
Priced moderately for Level 3 validation, it’s cost-effective for compliance-driven sectors (e.g., defense, finance). Competitors at this tier often require software installations or lack true cross-platform independence, adding hidden costs.
Strengths and Weaknesses:
Strengths: FIPS 140-2 Level 3 certified; no software/drivers needed; tamper-proof construction; separate admin/user PINs; reliable cross-OS support.
Weaknesses: Modest 32GB capacity; slower write speeds than SSDs; minimalistic interface may confuse new users.
Bottom Line:
A gold standard for uncompromising security in regulated environments. Highly recommended where certification and host isolation are non-negotiable, despite capacity limits.
9. Kingston Ironkey Locker+ 50 32GB Encrypted USB Flash Drive | USB 3.2 Gen 1 | XTS-AES Protection | Multi-Password Security Options | Automatic Cloud Backup | Metal Casing | IKLP50/32GB,Silver

Overview:
This USB drive merges hardware encryption with cloud integration, featuring XTS-AES 256-bit security and automatic backups—a hybrid solution for users balancing local and remote data safety.
What Makes It Stand Out:
The unique automatic cloud backup (via optional service) syncs files securely offsite, while a virtual keyboard blocks screenloggers. BadUSB attack protection and a rugged metal casing add physical/digital resilience uncommon in sub-$100 drives.
Value for Money:
Mid-range pricing is justified by cloud features absent in rivals like Apricorn. Though capacity is limited (32GB), the backup convenience and 145MB/s speeds offer tangible productivity gains for frequent travelers.
Strengths and Weaknesses:
Strengths: Cloud backup integration; virtual keyboard security; strong metal build; fast read/write speeds; multi-password complexity.
Weaknesses: Cloud backup requires subscription; capacity lags behind SSDs; no FIPS 140-2 validation; admin features need setup.
Bottom Line:
Excellent for mobile professionals needing encrypted local storage with cloud redundancy. Choose this over pure hardware drives if automated backups justify the subscription cost.
10. DataLocker H350 1TB External Hard Drive with Encrypted Password Protection, FIPS 140-2 Level 3 Certified, NATO Certified, TAA Compliant, AES 256-bit HDD Storage Suits Windows & macOS, Multi-Language

Overview:
A rugged, high-capacity encrypted HDD built for enterprise and government use, featuring FIPS 140-2 Level 3 validation, TAA compliance, and NATO certification—signifying top-tier security assurance.
What Makes It Stand Out:
The tamper-evident aluminum casing and SafeConsole remote management (e.g., device detonation, audits) cater to large deployments. TAA compliance and U.S. assembly meet strict procurement rules, while 1TB capacity suits multimedia workflows.
Value for Money:
Premium-priced but indispensable for federal contractors. Competing 1TB encrypted drives rarely combine Level 3 validation, TAA compliance, and remote management—making it cost-effective for regulated entities despite the $400+ tag.
Strengths and Weaknesses:
Strengths: 1TB storage; FIPS 140-2 Level 3 + NATO certified; TAA-compliant/U.S. made; SafeConsole management; USB 3.2 speed.
Weaknesses: SafeConsole license sold separately; heavy for portability; HDD (not SSD) speeds; complex setup for non-IT users.
Bottom Line:
The definitive choice for government/military teams requiring auditable, remotely manageable security at scale. Worth every penny where compliance is mandatory.
Why Business-Grade Encryption Isn’t Optional Anymore
The Escalating Cost of Data Breaches in 2026
The financial and reputational damage from a single data breach has skyrocketed, with 2026 seeing average costs far exceeding previous years. Fines under global regulations like GDPR, CCPA, and emerging frameworks now represent just the tip of the iceberg; mandatory client notifications, forensic investigations, and long-term brand damage create a perfect storm. Unencrypted portable storage remains a top vector for these incidents, making robust encryption not merely advisable but a fundamental fiduciary responsibility for any organization handling sensitive information.
Regulatory Landscapes Demand Proactive Measures
Compliance isn’t static, and 2026 brings stricter interpretations and expanded scopes for regulations worldwide. Industries like finance, healthcare, and legal services face heightened scrutiny where demonstrable, hardware-enforced encryption is increasingly mandated, not just recommended. Simply stating you have encryption isn’t enough; auditors now demand proof of validated, tamper-resistant implementations meeting specific standards (like FIPS 140-3), shifting the burden firmly onto businesses to choose solutions with verifiable credentials.
Beyond Compliance: Building Client and Partner Trust
In an era where data stewardship is a key differentiator, clients and partners actively vet vendors’ security postures. Utilizing visibly robust, independently certified encrypted storage signals professionalism and commitment to data integrity. This tangible demonstration of security hygiene fosters deeper trust, potentially becoming a decisive factor in winning contracts or maintaining critical partnerships, especially in sectors handling highly sensitive third-party data.
Decoding Encryption: Hardware vs. Software Realities
Why Hardware Encryption is the Business Standard
Hardware-based encryption, where the cryptographic engine is embedded directly into the drive’s controller chip, offers critical advantages for business use. It operates independently of the host computer’s OS, providing consistent, OS-agnostic security that’s immune to malware targeting software encryption layers. Crucially, the encryption key never touches the host system’s memory, significantly reducing attack surfaces and ensuring performance isn’t bogged down by CPU-intensive software processes—essential for handling large datasets common in business environments.
The Critical Role of Secure Key Management
The strength of any encryption hinges on how keys are generated, stored, and accessed. Business-grade solutions employ dedicated, tamper-resistant secure elements (often certified to Common Criteria EAL4+ or higher) to safeguard keys. Look for implementations where keys are generated on-device during initialization and never exposed externally, preventing extraction even if physical access to the drive is gained. Robust key management protocols are non-negotiable for true security.
Understanding Authentication Layers and Access Control
Strong encryption is only as good as its access controls. Modern business drives go beyond simple passwords, often incorporating multi-factor authentication (MFA) options like biometric readers (fingerprint) or PIN pads directly on the device. Granular access control features—such as multiple user profiles with distinct permissions (admin vs. read-only) and forced password complexity policies—are vital for managing diverse team access while maintaining an audit trail of usage.
Essential Features for Business Deployment and Management
Centralized Admin Console Capabilities
For organizations deploying multiple drives across teams or locations, the ability to manage devices centrally is transformative. Seek solutions offering a dedicated admin console (cloud-based or on-prem) enabling remote policy enforcement, password resets, drive status monitoring, and detailed audit logging. This capability drastically reduces IT overhead, ensures consistent security posture enforcement, and provides crucial visibility during incident response.
Audit Logging and Tamper Evidence
Comprehensive, tamper-proof audit logs recording every access attempt (successful or failed), password changes, and administrative actions are indispensable for compliance and forensic analysis. True business-grade drives store these logs securely within the device’s protected environment. Additionally, physical tamper-evidence features—like seals that irreversibly indicate casing intrusion—are critical for verifying device integrity after potential physical compromise.
Seamless Integration with Existing IT Ecosystems
The drive shouldn’t exist in a security silo. Evaluate how well potential solutions integrate with your current directory services (like Active Directory or Azure AD) for user management, endpoint security platforms for policy enforcement, and backup/recovery systems. Compatibility with standard business operating systems (Windows, macOS, Linux) without requiring complex drivers or agent software ensures broad usability and minimizes deployment friction.
Performance and Reliability: Non-Negotiables for Business Continuity
Sustained Throughput for Large Data Workloads
Businesses constantly move massive files—video assets, complex financial models, engineering CAD files. Encryption must not cripple performance. Prioritize drives utilizing high-speed interfaces (USB 4, Thunderbolt 4) paired with hardware encryption engines designed for minimal latency. Look for sustained read/write speeds that meet or exceed your typical workload demands, ensuring encryption doesn’t become a bottleneck during critical data transfers or backups.
Ruggedized Design for Real-World Demands
Business drives travel—between offices, job sites, client meetings, or to offsite storage. They need to withstand drops, vibrations, dust, and temperature fluctuations far beyond consumer-grade expectations. Evaluate ingress protection ratings (IP ratings), shock resistance certifications (like MIL-STD-810H), and overall build quality. A drive that fails physically under field conditions is just as vulnerable as an unencrypted one.
Long-Term Data Integrity and Endurance
Beyond speed, consider the drive’s endurance (terabytes written - TBW) and error correction capabilities. Business data often has a longer active lifecycle; robust error-correcting codes (ECC) and wear-leveling algorithms are essential to prevent silent data corruption over time, especially with frequent writes. Verify warranty periods and the manufacturer’s reputation for long-term reliability and data recovery support.
Navigating Compliance and Certification Requirements
Demystifying FIPS 140-3 Validation
The Federal Information Processing Standard (FIPS) 140-3 is the gold standard for cryptographic module validation, increasingly required beyond just government contractors. Validation at Level 2 or higher (requiring role-based authentication and physical tamper-evidence) provides independent, rigorous assurance that the encryption implementation meets stringent security requirements. Never assume “military-grade” claims equate to FIPS validation—always demand the specific certificate number and level.
Industry-Specific Compliance Considerations
Depending on your sector, additional frameworks may apply. Healthcare entities must ensure solutions support HIPAA’s technical safeguards for portable media. Financial institutions face FFIEC and GLBA mandates. Global businesses need solutions that facilitate adherence to GDPR’s “appropriate technical measures” clause for data portability. Understand which specific clauses your industry regulations impose on portable storage and verify how candidate drives address them.
The Importance of Third-Party Security Audits
Beyond self-certification or basic compliance claims, look for vendors who proactively subject their encryption modules and firmware to independent, adversarial security audits by reputable firms. Reports from such audits, even if redacted, provide invaluable transparency into the solution’s real-world security posture and the vendor’s commitment to ongoing vulnerability management.
Implementation Strategies for Maximum Security
Establishing a Clear Portable Media Policy
Technology alone isn’t the solution; it must be backed by a well-defined, enforced policy. Your policy should dictate when encrypted drives must be used, acceptable encryption standards, secure handling procedures (never leaving drives unattended), mandatory password policies, and protocols for drive decommissioning. Regular employee training on this policy is as crucial as the drive itself.
Secure Onboarding and Initialization Procedures
The initial setup of an encrypted drive is a critical vulnerability window. Implement strict procedures: initialization must occur on a clean, trusted machine; strong, unique admin passwords must be set (never default); and multi-factor authentication should be enabled immediately. Avoid ad-hoc setup by individuals—central IT should control the initial configuration process to ensure standards are met.
Decommissioning and Secure Data Erasure
When a drive reaches end-of-life or is reassigned, secure data erasure is paramount. Business-grade solutions offer certified cryptographic erasure (instantly rendering data unrecoverable by destroying the key) or secure physical destruction protocols. Documented procedures for decommissioning, including verification steps, are essential for compliance and preventing data leakage from retired assets.
Future-Proofing Your Investment
Preparing for Post-Quantum Cryptography (PQC)
While large-scale quantum computers capable of breaking current encryption (RSA, ECC) aren’t mainstream in 2026, forward-thinking businesses are evaluating solutions with upgradeable firmware or architectures designed for PQC algorithm integration. Understanding a vendor’s roadmap regarding NIST-standardized PQC algorithms (like CRYSTALS-Kyber) is becoming a strategic differentiator for long-term data security.
Cloud Integration and Hybrid Work Realities
The line between portable storage and cloud sync blurs. Consider drives that offer seamless, encrypted integration with your business cloud storage platforms, allowing secure local caching and offline access without compromising data security during sync. This supports modern hybrid work models while maintaining control over sensitive data residing on the portable device.
Evaluating Vendor Longevity and Support Commitment
Choosing a vendor is a long-term security partnership. Assess their track record in security research, responsiveness to vulnerabilities (check their CVE history), commitment to firmware updates, and the depth of their enterprise support offerings (SLAs, dedicated contacts). A solution from a vendor with shallow pockets or poor security hygiene creates future risk, regardless of current features.
Frequently Asked Questions
Why can’t I just use free software encryption like VeraCrypt for business drives?
Software encryption relies on the security of the host operating system, which is vulnerable to malware and exploits. It lacks hardware-enforced tamper resistance, consistent cross-platform performance, and centralized management features essential for business accountability and compliance. Key handling is also less secure within the host OS memory.
How do I verify if a drive’s encryption is truly FIPS 140-3 validated?
Visit the official NIST CMVP (Cryptographic Module Validation Program) website and search the validated modules list using the vendor’s name and specific module certificate number. Never rely solely on vendor marketing claims; the NIST list is the definitive source.
Is biometric authentication on a drive secure enough for business use?
Biometrics (like fingerprint readers) add a strong layer of convenience and security when implemented correctly within a hardware-secured environment. However, they should ideally complement, not replace, strong PIN/password authentication (multi-factor), and the biometric template storage must occur within the drive’s secure element, not the host PC.
What’s the biggest mistake businesses make when deploying encrypted drives?
The most common critical error is neglecting a comprehensive policy and employee training. Technology fails without proper procedures for initialization, secure handling, password management, and decommissioning. Assuming the drive alone solves the problem leads to security gaps.
How often should encrypted drives be replaced or have their firmware updated?
Follow the manufacturer’s recommended lifespan (often 3-5 years for heavy use) and immediately apply critical security firmware updates. Proactively monitor vendor security advisories. Drives showing physical wear, performance degradation, or failing self-tests should be decommissioned securely.
Can I use the same encrypted drive for both Windows and Mac computers?
Yes, but only if the drive uses hardware encryption with cross-platform compatibility (no OS-specific software drivers required). Verify explicit support for all target operating systems (Windows, macOS, Linux) in the specifications, as some solutions may have limitations or require different initialization steps.
What does “cryptographic erasure” actually mean for decommissioning?
Cryptographic erasure instantly and irreversibly destroys the encryption key stored securely within the drive’s hardware. Without this key, the encrypted data becomes permanently inaccessible gibberish, offering a far faster and more verifiable method than traditional multi-pass overwriting, especially for large drives.
How do I enforce strong password policies across multiple encrypted drives?
This requires a solution with a centralized management console. Through the console, administrators can set mandatory password complexity rules (length, character types), enforce regular rotation schedules, lock out users after failed attempts, and remotely reset passwords, ensuring uniform policy enforcement.
Are self-encrypting drives (SEDs) sufficient, or do I need “hardware encrypted” specifically?
All true business-grade hardware-encrypted drives are Self-Encrypting Drives (SEDs). The key distinction is ensuring the SED meets business requirements: FIPS validation, tamper resistance, secure key management, and robust authentication. Not all SEDs (especially basic consumer models) offer these enterprise features.
How do I balance security with the need for employees to easily access data on the go?
Prioritize solutions with intuitive, secure access methods like fast biometrics or PIN pads directly on the drive, eliminating cumbersome software logins. Ensure seamless cross-OS compatibility and high-speed interfaces to prevent security from becoming a productivity barrier. Strong user training on secure handling practices is equally vital.